YAML Preflight
Validate strict YAML, duplicate keys, and common GitHub Actions permission mistakes locally in your browser.
About YAML Preflight
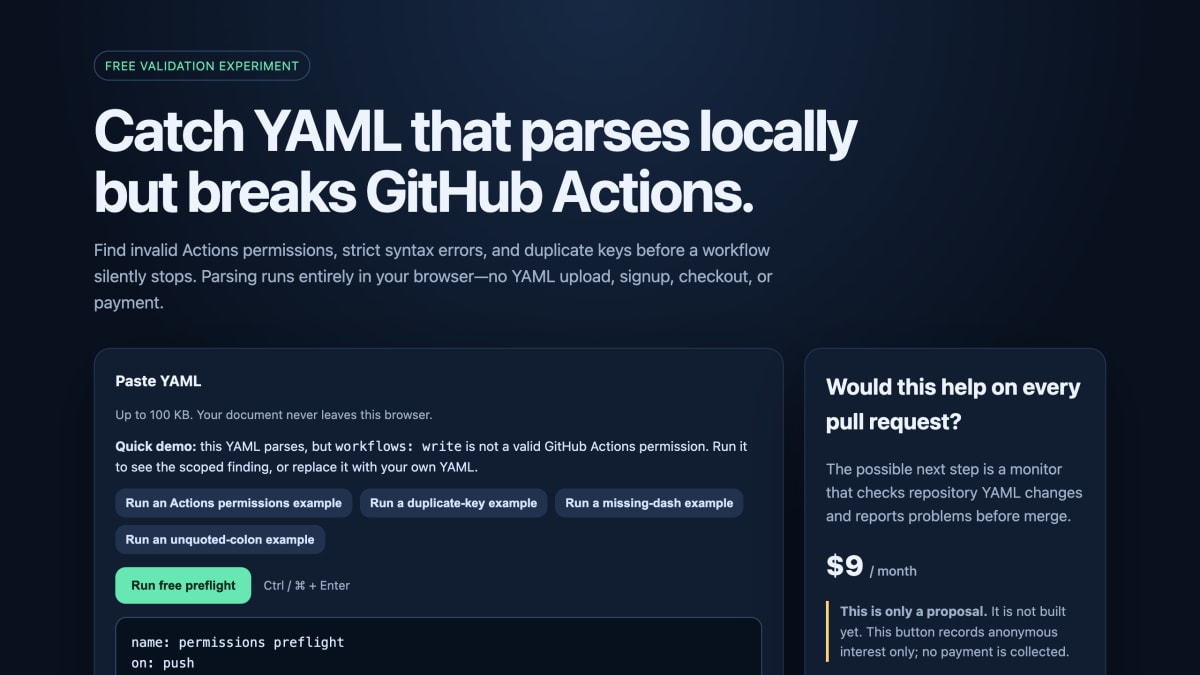
YAML Preflight is a browser-based tool for validating YAML files intended for use in GitHub Actions workflows. It checks for issues that pass standard YAML parsing but cause problems in GitHub Actions specifically, including invalid Actions permissions values, strict syntax errors, and duplicate keys. Parsing and validation run entirely client-side, with no upload, signup, checkout, or payment required to use the tool.
The tool accepts pasted YAML up to 100 KB and displays a parsed preview alongside any findings. It includes preset examples demonstrating specific error types: invalid Actions permissions, duplicate keys, missing dashes, and unquoted colons. It is aimed at developers who want to catch workflow-breaking YAML errors before committing changes that could cause a GitHub Actions workflow to fail silently.
The page also proposes a paid follow-on feature, a monitor that would check repository YAML changes and report problems before merge, priced at $9/month. This feature is not built; a button on the page records anonymous interest in it without collecting payment. The product is built by aevumere.
Key features
- Validates YAML syntax and flags strict parsing errors like duplicate keys and missing dashes
- Checks GitHub Actions permissions blocks against valid permission scopes
- Detects unquoted-colon and other common YAML formatting mistakes
- Runs entirely client-side in the browser with no upload, signup, or payment required
- Shows a parsed YAML preview after validation
Frequently asked questions
Is YAML Preflight free to use?
Yes, the current validation tool is free with no signup, checkout, or payment required.
Does it upload my YAML to a server?
No, parsing and the permissions check run entirely in your browser and the document never leaves it; only an anonymous pass/attention outcome is sent to measure the experiment.
What kinds of YAML problems does it catch?
It catches invalid GitHub Actions permissions, strict syntax errors, and duplicate keys, plus examples like missing dashes and unquoted colons.
Does it fully validate the GitHub Actions workflow schema?
No, the permissions check does not claim full GitHub Actions workflow-schema validation.
Is there a paid tier or upcoming product?
A proposed $9/month monitor that checks repository YAML changes on every pull request is planned but not yet built; the current page only collects anonymous interest.

SerpApi - Search API
SerpApi's Search API makes it easy and fast to scrape Google and other search engines.

Show your product to thousands of developers
· 100k monthly pageviews
· 7k newsletter subscribers
You might also like
TestingBot
TestingManual and Automated testing on 5000+ browsers and mobile devices online. Make sure your website and mobile app looks and functions correctly on all devices. Free 14 day trial.
TestingWhiz
TestingExperience effective test automation of web & mobile apps with an easy & intuitive codeless end-to-end software testing tool, TestingWhiz. Download 30-days free trial.
TestSprite
Testing/AI/ToolingThe most powerful AI testing tool for testing, fixing, and validating your software in one automated flow.
ValidateHTML
Testing/Tooling/SEOFree online validation tools for HTML, CSS, JSON, XML, meta tags, and Open Graph. Get instant quality scores from 0 to 100.
Velocity
UX/Prototyping/TestingOn-demand feedback for Figma prototypes.
Xray
TestingThe #1 Manual & Automated Testing App for Jira. Plan, Execute and Track your Quality Assurance with Requirements Traceability.